Imagine receiving an email from your bank informing you that your personal data, contact addresses, identification documents, and financial data (including transaction history) are now in the hands of a hacker.
Read more CO2 tax: first approval for finished products, but the clause on price increases is dropped
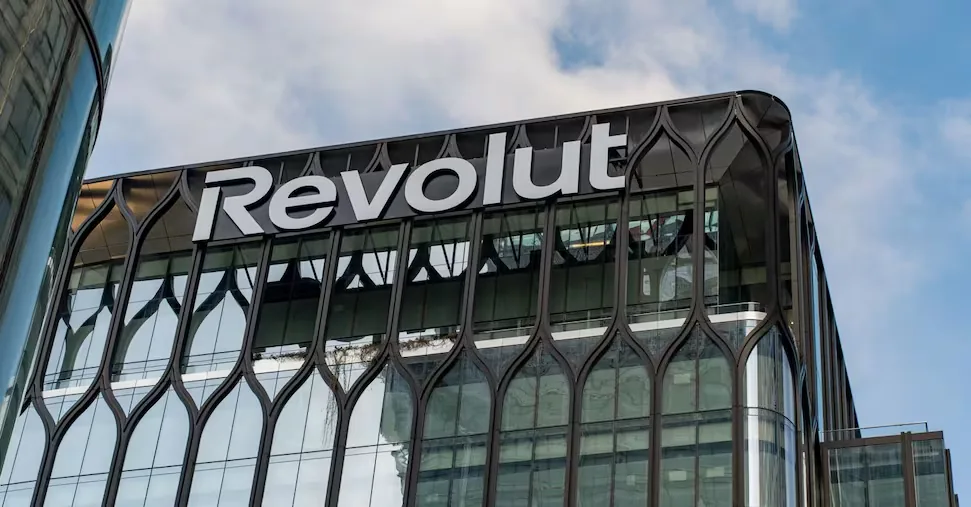
This is what happened to several Revolut customers, estimated to be just under 700 people. The British fintech company notified the affected users via email: “We contacted you to inform you of a recent security incident, consisting of an external identity theft that caused some of your personal data to be shared with an unauthorized third party.”
What happened
Revolut stated that it received a data sharing request for its customers from an account that appeared to belong to a government body. The company proceeded by forwarding the requested information, as established by the GDPR (General Data Protection Regulation). According to the European regulation, a company is required to forward its customers’ personal data if the request from the government entity is binding, formally legitimate, and based on specific legal provisions (such as investigation orders or warrants).
Read more US Weapons in Space: Strong Reaction from Beijing and Moscow
“The data request procedure by a government company is called ‘Emergency data request’ and all platforms (social networks, cloud providers) handle dozens of them on a daily basis,” explains Marco Ramilli, founder of the Italian cybersecurity company Yoroi.
The problem? The requester was not really a public authority. The hackers acted under false pretenses, using an address actually belonging to the email domain of a government entity and therefore with valid authentication credentials.
Read more Foreign interference, Fdi and Lega vote with Vannacci and the M5S against the creation of a center …